Skip to content
EliTechZ homeMenu
Pulse 14
Close the security events
EliTechZ Security Pulse 24HClose security events
SQL injection3
XSS0
Brute force0
Scans / fuzzing0
Incoming DMARC (recorded incoming DMARC failures)0
Domain DMARC (reported domain DMARC failures by Cloudflare receipt time)0
Other web events11
Top web-event countriesUS (5), DE (4), BE (2)
· 24h security snapshot across the EliTechZ estate.

01 / 04EliTechZ

Infrastructure + offensive security

Elite IT
A-Z. Cloud Infrastructure & Offensive Security

Infrastructure that performs.
Security that holds.

EliTechZ is an engineering and security company in Hilversum, the Netherlands. When a platform is unreliable or a security question keeps coming back, you need someone who can get into the detail and own the work. As architect and consultant, EliTechZ designs and builds the fix, tests it and shows your team how to run it.
The EliTechZ storyCompany film
From pressure to progress.Sound on for the full story

Be in control. Keep the platform running without losing sight of cost or risk.

Explore the security perspective

Cloud infrastructure.
AI integration.
Offensive security.

A cloud migration or security redesign is hard to undo. We work through the trade-offs with your team before changing the platform, then test the result.

Your team should understand what changed and how to look after it. Our experience includes European e-commerce logistics, media, broadcast and streaming platforms.

Trusted by
Platforms that support the business
Cloud, on-premises or hybrid: the platform has to work on a difficult day, not just at launch. We account for access, networking, monitoring and recovery while building it.
AI integration & automation
AI should make a real task easier. We connect it to your workflow, limit what data it can reach and agree where a person needs to check the output.
Security built into delivery
Security is part of the build. We set sensible defaults, test what could go wrong and check that the changes actually help.
A solution your team can own
We build the platform, prove it works and explain it to the people who will run it. They should not have to call us just to understand the next change.
More about EliTechZ We stay until your team can run the result, from cloud platforms to business WiFi.

Elite IT A-Z means staying with the work until your team can run the result. That might mean untangling a cloud platform or sorting out the basics, such as business WiFi, remote access or storage. We can discuss EU hosting and relevant GDPR or NIS2 requirements when they affect the design.
02 / 04Infrastructure

Cloud · platform · identity

Cloud & platform
engineering.

Resilient platforms.
Secure identity. Calm operations.

A platform can look sound on paper and still be painful to operate. We work across cloud, hybrid and on-premises systems, connecting identity, automation and monitoring to the way your team actually runs them. AI integration is considered where it solves a useful problem.

From complexity to controlInfrastructure film
Build. Automate. Observe. Improve.Sound on for the full story

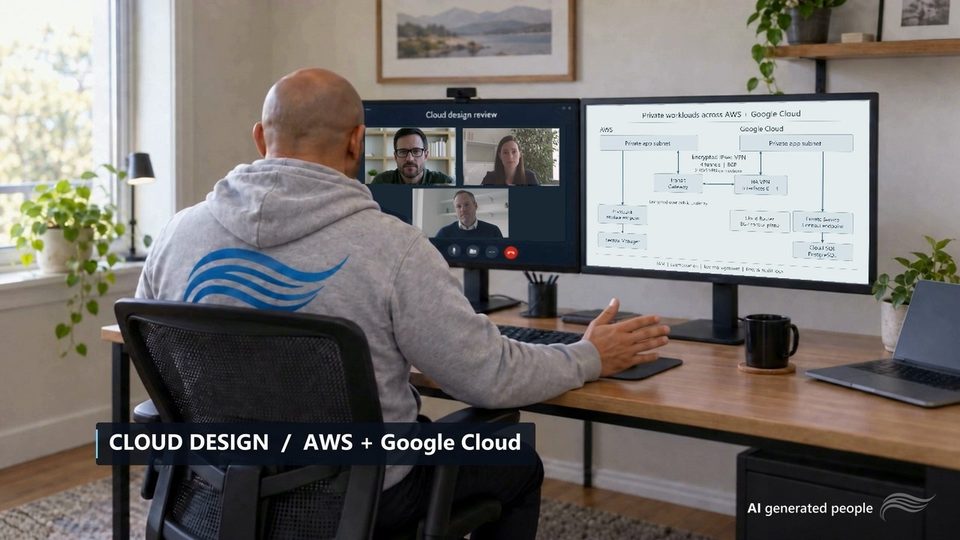
Across your estate. AWS, Azure, GCP, Kubernetes, VMware, Nutanix, Proxmox and Oracle.

Start with your environment

Practical engineering.
From foundation to operation.

Start with the issue that is costing your team time. If it points to a wider problem, we can look at the architecture together.

Blue team & incident response
When an incident happens, the first job is to understand it. We use tools such as Microsoft Sentinel and KQL to investigate, then strengthen the controls that would help you spot or contain a repeat.
AI integration & workflow automation
We start with the task you want AI to improve, not the model you want to use. Once it is connected to your application, we check its output, restrict data access and make sure someone owns it after launch.
Kubernetes, migration & automation
Moving a workload is only useful if the new environment is easier to run. We build cloud foundations and Kubernetes platforms on AKS, EKS, GKE or on-premises systems, using Terraform, Ansible and Helm to make changes repeatable.
Virtualization & private cloud
We work with Nutanix, VMware vSphere and Proxmox estates, from platform changes to recovery and capacity planning. We also support virtual desktops and remote applications with Citrix, Horizon, Azure Virtual Desktop, RDS and NVIDIA GRID/vGPU.
Networks, email & workplace
We help with email migrations, authentication and delivery, alongside networks, firewalls, SD-WAN and WiFi. Endpoint security and zero-trust access keep the people using those systems connected with appropriate permissions.
CCTV, access control & building systems
CCTV and door-access systems need reliable networks and storage. We help keep them separate from general business traffic and make maintenance access deliberate rather than always open.
Monitoring, observability & FinOps
A dashboard is useful only when someone knows what to do with it. We use Grafana, Prometheus and Loki to make problems visible, tune alerts to reduce noise and relate the signals to reliability and cloud spend.
Storage, media & recovery
We work on shared storage, media production systems and the backups behind them. That includes performance and capacity checks, Adobe and Avid workflow integration, and testing whether a restore works as expected.

Infrastructure case studies

Examples of platform improvements delivered by EliTechZ. Client details are omitted; results depend on the environment.

Active Directory hardening NTLMv1 is off, service accounts became gMSAs and reliance on shared passwords dropped.

Older authentication: Older authentication was still in use, and service accounts carried more access than they needed.

Identity hardening: We moved services off NTLMv1, then disabled NTLMv1 authentication. Service accounts were converted to group Managed Service Accounts (gMSAs). Where a writable domain controller was not needed, we used a read-only one, and we raised the functional level to Windows Server 2025. We also separated storage and client settings in Group Policy and replaced startup scripts with policy-based configuration.

Reduced password reliance: Less reliance on legacy authentication and shared passwords. The new Group Policy structure is easier for the team to understand and maintain.

Zero-trust microsegmentation Each microservice now reaches only the data it needs, and broadcast traffic fell.

Excess network access: Services could reach parts of the network they had no reason to talk to. That made a single breach harder to contain.

Service boundaries: We put zero-trust controls at the front end and limited each microservice to the data services it actually needed. Terraform and Kubernetes made the boundaries repeatable. Monitoring and security reporting still had to work after the change.

Fewer unnecessary paths: Services had fewer unnecessary network paths. Broadcast traffic fell, and the team kept the visibility it needed to operate the platform.

Azure network performance Production speed rose a further 22% after NIC driver updates and MTU tuning.

Slow production networks: Network performance on the Azure virtual machines was holding production back.

Driver and MTU changes: We updated the NIC drivers across the estate to supported versions and tuned MTU settings, including jumbo frames where appropriate.

Performance improvement: Production speed improved by a further 22% in that environment.

From assessment to a platform you can operate Your cost of downtime sets the priorities, and every change is recorded with its reason.
  1. Agree the priorities. Review workloads, dependencies, current failures and the cost of downtime. Agree the scope and what a successful result looks like.
  2. Build and document. Deliver the agreed migration, configuration or automation, with a record of what changed and why.
  3. Check the result. Validate the changes against the agreed requirements, including monitoring and recovery where they are in scope.
  4. Hand over. Give your team the operating documentation and practical knowledge to manage the platform, alerts and future changes.
CCTV and connected building security A camera is no use if its storage fails, so we check what happens when power is lost.

A camera is no use if its recording network or storage fails. We look at the infrastructure behind CCTV and door access, including what happens when power or connectivity is lost.

We keep building systems apart from ordinary office traffic and agree who can access recordings or maintain devices. Retention and recovery are discussed with the building owner and relevant specialists.

Platforms and specialist capabilities From AWS and Kubernetes to AIX and mainframes, we support the systems you already use.

We support the systems your team already uses. The scope may be a migration, a reliability problem, a security change or day-to-day administration.

These are platforms and tools we work with. We agree the environment, access and deliverables before starting, including any mainframe or specialist media work.

  • Cloud and virtualization: AWS, Azure, GCP, Oracle, OpenStack, Nutanix, VMware vSphere/ESXi and Proxmox.
  • Containers and automation: Kubernetes, AKS, EKS, GKE, Red Hat OpenShift, Nutanix Kubernetes Platform, Harbor, Terraform, Ansible, Helm, PowerShell, Bash, GitHub workflows and Azure DevOps.
  • AI platforms and integration: Ollama, OpenAI, Anthropic Claude and Google Gemini; model integration, agreed data access and human review.
  • Networks and firewalls: Juniper, Check Point, Cisco, Fortinet, Palo Alto Networks, UniFi, OPNsense, pfSense, OpenWrt, SD-WAN, NGINX and Traefik.
  • Email security and authentication: Barracuda, FortiMail, Proofpoint, Red Sift and Valimail; SPF, DKIM and DMARC.
  • Email platforms and clients: Microsoft 365 (Office 365), Google Workspace, Zoho Mail, Proton Mail, Spark Mail, Microsoft Exchange and self-hosted mail.
  • Endpoint security and management: Microsoft Defender for Endpoint, CrowdStrike, Trend Micro, FortiClient EMS, Carbon Black, Microsoft Intune, ManageEngine Endpoint Central and NinjaOne.
  • Zero-trust network access (ZTNA): Zscaler, Twingate, Tailscale, Akamai Enterprise Application Access (EAA), Cloudflare and Fortinet.
  • Virtual desktops and remote applications: NVIDIA GRID/vGPU, Microsoft Remote Desktop Services (RDS) and Terminal Server, Azure Virtual Desktop, Omnissa Horizon (VMware Horizon) and Citrix.
  • Storage: Pure Storage, Qumulo, Dell ECS, Isilon, NetApp, Synology, QNAP, Avid NEXIS and Avid ISIS.
  • CCTV and building systems: Hikvision CCTV, with supporting network, storage and access-control infrastructure.
  • Media workflows: Adobe, Avid and Final Cut Pro; workstation, storage and broadcast workflow integration.
  • Operating systems and enterprise platforms: Windows, Windows Server, macOS, Debian, Ubuntu, Red Hat, Unix and AIX, plus mainframe support.
  • Backup and recovery: Veeam, Cohesity, recovery planning and restore validation.
  • Monitoring and incident response: Grafana, Prometheus, Loki, Elastic Stack (ELK), Splunk, Nagios, ManageEngine OpManager, Microsoft Sentinel, Exabeam, Rapid7 and KQL.
  • Identity and secrets: Active Directory, IAM, Conditional Access, gMSA and HashiCorp Vault.
  • Application and database troubleshooting: Microsoft SQL Server, MySQL and MongoDB; tracing faults across applications, databases and infrastructure.
The engineer behind the work ISC2 and Nutanix certified, with Maersk awards for customer support and problem solving.

EliTechZ delivers infrastructure, automation and offensive security work, from the first design decisions through implementation and handover. The engineer delivering these services has experience in European e-commerce logistics, media, broadcast and streaming platforms.

Earlier engineering roles included company and tenant migrations, storage and recovery projects, broadcast and streaming operations, and troubleshooting across applications, databases and infrastructure. That experience informs the work delivered through EliTechZ today.

Engineering portfolio on GitHub. Public responsible disclosure acknowledgements are listed in the Red Team section.

Individual qualifications

Qualifications earned by the engineer delivering EliTechZ services include ISC2 Certified in Cybersecurity, Microsoft Certified: Azure Fundamentals (AZ-900), ITIL Foundation, and Nutanix Associate and Professional certifications covering multicloud infrastructure, cloud integration, business continuity, and network security.

Achievements include PRINCE2 Foundation in 2019 and Microsoft Windows 7 specialist certifications in desktop support and configuration in 2015.

Training and professional recognition

Completed Architecting on AWS and Migrating to AWS courses, plus Syberwise industrial control system (ICS/SCADA) security learning through beginner and intermediate quiz levels.

Individual professional recognition includes Maersk STARS and SPOT awards for customer support, collaboration, and problem solving.

Platform updates and source feeds Kubernetes, GitHub Docs and Proxmox release news in one place, refreshed every day.

The latest items from the Kubernetes, GitHub Docs and Proxmox release feeds, refreshed daily. Each entry keeps its original publication date and links to the source, with the feed’s licence noted beneath it.

03 / 04Red Team

Offensive security · vulnerability testing

Penetration testing.
Red teaming.

Offensive security that gives
your team a clear next step.

Penetration testing should tell you what someone could actually reach, not just produce a list of warnings. We test the agreed systems, explain what we could demonstrate and help your team decide what to fix first.

A different perspective on riskSecurity film
Test the path. Validate the impact.Sound on for the full story

Evidence that leads to action. See what was found, why it matters and whether the fix holds.

Define the scope together

Understand the exposure.
Know where to act.

We follow realistic attack paths within the agreed scope. The report should make sense to the engineer fixing the issue and the person deciding what to tackle first.

Partnered with

Web, API & cloud
We test whether a flaw in a web app, API or cloud service could lead to something important. Findings are ranked by what we could demonstrate, not by a generic severity label alone.
AI penetration testing
An AI feature may handle untrusted text or have access to tools it does not need. We test those boundaries, explain the risk and check the changes when a retest is agreed.
Identity & Active Directory
Identity controls matter most when an ordinary account is compromised. We look for routes to wider access in IAM and Active Directory, then check whether hardening closes them.
Applications, binaries & mobile
We examine how an application handles access and stores data, including what can be learned from its binaries or mobile app. The report tells your developers what needs attention.
Device & hardware security
For routers and embedded devices, we agree what can be tested before touching the hardware. The depth of a firmware or chip-level review depends on the device and the permissions available.
Physical & building security
A physical review looks at the agreed building and how access works in practice. That may include visitor entry, CCTV coverage and who responds when something goes wrong.
Deliverables that support decisions
You get a plain-English account of what we found and why it matters, backed by evidence your team can use. We agree what to fix first and can retest the changes.

Security assessment case studies

Examples of authorized assessments and the decisions they supported. Client identities and sensitive technical details are kept private.

Lost-device resilience assessment On a laptop left behind, file controls held but monitoring and permissions needed fixes.

A laptop left behind: The question was simple: what would be exposed if a managed laptop was left behind?

Access and monitoring tests: We tested the device and followed the access available from it, checking whether monitoring would alert the team and whether cloud files stayed protected.

Data and monitoring findings: On-demand file controls limited access to user data. Monitoring and application permissions needed attention, so the team received a clear order for the fixes.

Azure third-party access assessment The client's own controls were strong, but its IT partner's way in needed tightening.

Outside support access: The organization had put strong controls around its own Azure accounts. It wanted to know whether outside support access was held to the same standard.

Partner access review: We reviewed the agreed Azure environment, including how its IT partner could reach supported services.

Controls needing attention: The internal controls held up well. A third-party support route needed tighter access controls.

AI application: recruitment platform Untrusted CV content changed the LLM summaries in ways the hiring team did not expect.

AI-generated CV summaries: A recruitment team used an LLM to turn CVs into short summaries.

Untrusted content test: We checked what happened when the application passed untrusted CV content to the model.

Unexpected summaries: The content changed the summaries in ways the team did not expect. We recommended clearer input boundaries and a person checking the result.

Responsible disclosure and security recognition Experience that includes NCSC-NL acknowledged disclosures and an April 2026 SPOT award.

The experience behind EliTechZ includes responsible vulnerability disclosures acknowledged by NCSC-NL and an April 2026 SPOT award for identifying and responding to a significant security threat.

How an assessment is scoped and verified Agreed limits protect live operations, and a prioritized plan shows what to fix first.
  1. Set the boundaries. Agree systems or premises, objectives, written permission, timing and limits that protect live operations.
  2. Test and record. Examine the agreed attack paths and record what the evidence demonstrates, including relevant limits.
  3. Explain what to fix. Deliver an executive summary, reproducible technical findings and a prioritized remediation plan.
  4. Verify the fixes. If a retest is agreed, revisit the affected controls and report whether the original findings are resolved.

For a building review, the agreed scope can cover entry, CCTV, connected devices and response responsibilities.

Public profiles and responsible disclosure Individually acknowledged by Microsoft, NASA, TU Delft and the Netherlands Tax Administration.

Responsible disclosure acknowledgements

Responsible disclosure work by the engineer behind EliTechZ is acknowledged on the following organisations' public pages. These are individual research acknowledgements.

Oasen · DMC Group · Netherlands Tax Administration · Microsoft Security Response Center · Utrecht University · Wageningen University & Research · Lentiz · TU Delft · Radboud University · Informatiebeveiligingsdienst.

Individual NASA appreciation letters received in 2024 also recognise responsible vulnerability disclosure.

Security research and continuous learning

Bugcrowd research profile · TryHackMe training profile.

Hands-on practice includes security labs and CTFs. The public profiles provide a view of ongoing activity.

Security advisories and source feeds Fresh NVD CVEs plus CERT-EU and NCSC warnings arrive daily, each with its original date.

The latest advisories from the NVD, CERT-EU and NCSC feeds, refreshed daily. Each entry keeps its original publication date and links to the source, with the feed’s licence noted beneath it.

04 / 04Contact

Based in Hilversum · Netherlands + worldwide support

Be in control.
Start a conversation.

Tell us what is getting in the way.

You do not need a finished project plan. Tell us what is not working, what you have tried and what a good outcome would look like.

The simplest way to begin

A short email is enough. Tell us what is happening, which systems are involved and when you need help. Please leave passwords and sensitive data out of the first message.

Lijsterweg 65 · 1221 JH HilversumKVK 93985290 · Established 1 June 2024Google Maps · OpenStreetMap

Infrastructure. Security. Delivery. A connected view of the work ahead.

Revisit the EliTechZ story

Bring the question
that matters to your team.

You can start with a problem, not a project plan.

A platform needs attention
Perhaps the platform slows down at busy times, or the same incident keeps returning. Tell us what happens and when.
A migration is coming
Moving to cloud or changing identity systems affects the people who use them. We can help plan the move without losing control of access or costs.
Security needs evidence
If you are unsure whether a control works, we can test it within agreed boundaries. You will know what to fix and whether the change helped.

How EliTechZ works

A clear start, regular updates and a handover your team can use.

1. Scope
We agree what needs to change, what is in scope and what your team will receive. For security testing, written permission comes first.
2. Deliver
We do the agreed work and keep your team informed, especially if a finding changes the plan.
3. Validate
We check whether the change solved the problem and show you how we reached that conclusion.
4. Handover or retest
Your team gets what it needs to run the result. For security findings, we can test the fix again if that is part of the scope.

Frequently asked questions

Need help? .

What does EliTechZ do?

EliTechZ is an engineering and security company in Hilversum, the Netherlands. We build, fix and automate cloud and on-premises infrastructure, connect AI tools to business workflows and test security through penetration testing and red teaming.

Which service fits my situation?

Infrastructure work fits when a platform is unreliable, needs to move or keeps causing trouble. Penetration testing or red teaming fits when you need to know how an attacker could reach something important. AI integration fits when you want AI tools in your workflows with clear permissions and a person checking the result.

What should I include in an enquiry?

Tell us what is happening, which systems are affected and when you need help. Please do not send passwords or sensitive data in your first email.

Why do you use email instead of a contact form?

There is no contact form, analytics or advertising tracking. Email us when you choose to. Cloudflare processes essential request data to deliver and protect the site.

How are scope and timelines agreed?

We put the work, price and timing in writing before we start. A security assessment also needs your explicit permission and clear limits.

How is confidential information handled?

We agree how to handle sensitive information before the work starts. If you need to send an encrypted security report, use the published PGP key and email our security contact.

What does cloud infrastructure delivery include?

It depends on what you need. We might build a new platform, fix an existing one or automate a task that keeps causing trouble. We test the result and make sure your team knows how to run it.

What does a penetration test or security assessment deliver?

You get a clear account of what we found, why it matters and what to fix first. The technical detail is there for the people doing the work.

Can penetration test findings be retested?

Yes, if it is part of the agreed work. We test the affected area again to see whether the original issue is resolved.

Can you work alongside our existing IT partner?

Yes. We agree who does what with your team and your provider before work begins.

Do you work outside the Netherlands?

Yes. We are based in Hilversum and work with teams in the Netherlands and elsewhere. We can discuss the project in English or Dutch.

Chromium HSTS preloadMozilla HTTP Observatory GradeW3C ValidationUptime Robot ratio (30 days)

No marketing tracking: This site does not use analytics, advertising pixels, or marketing cookies, and we do not set cookies for normal visits. The site is delivered and protected by Cloudflare (CDN / security), which processes basic request metadata (for example, IP address, user-agent, request path, and timestamps) to provide the service. Very rarely, Cloudflare may present a security challenge; if that happens, Cloudflare may set a short-lived, strictly necessary cookie to remember the challenge result and keep the site secure.

Hosting: The site is served via Cloudflare Pages. Cloudflare may process basic request metadata (for example, IP address, user-agent, and security-related logs) to deliver and protect the service. See Cloudflare’s Privacy Policy.

Films: Our films are hosted on YouTube and embedded in privacy-enhanced mode (youtube-nocookie.com), which uses YouTube API Services. Nothing is loaded from YouTube until you open a film. YouTube, a Google service, then receives basic request data such as your IP address and browser details, and may set cookies or use similar storage on its own domain. See the Google Privacy Policy.

Contact: If you have privacy questions, .

Cookies: We do not use cookies (or localStorage/sessionStorage) for analytics, advertising, or personalization, and we do not run third-party trackers. Cloudflare is configured to avoid cookies for normal visits, but in rare cases where Cloudflare serves a security challenge, it may set a short-lived, strictly necessary cookie (for example, a clearance cookie) so you can continue browsing without repeated challenges. Our films are embedded from YouTube in privacy-enhanced mode and load only when you open one; YouTube may then set its own cookies, as described in the Privacy Policy.

Consent notice: because no non-essential cookies or trackers are used, the on-page notice only stores your preference not to show the informational cookie/security notice again on later visits. That preference is stored in a small first-party __Host-cookie_consent cookie and is not used for analytics, advertising, or personalization.

If this changes in the future, we will request consent before setting any non-essential cookies or enabling any tracking technologies.

This website is provided “as is” for informational purposes. Content may change without notice.

No warranties: EliTechZ makes no warranties of any kind, express or implied, regarding accuracy, completeness, or fitness for a particular purpose.

Limitation of liability: To the fullest extent permitted by law, EliTechZ is not liable for any direct or indirect damages arising from use of this site.

External links: Links to third-party sites are provided for convenience; EliTechZ does not control or endorse their content.

Film playback: The films on this site play through YouTube. By playing a film you agree to the YouTube Terms of Service.

Requests & work: Any services are subject to a separate written agreement that defines scope, fees, timelines, and responsibilities.

Coordinated Vulnerability Disclosure (CVD)

Close Coordinated Vulnerability Disclosure and return to home

Even with strong controls, vulnerabilities can exist. If you discover an issue, please report it so we can address it quickly.

How to report

Please do

Please don’t

What we promise

Hall of Fame 🏆

Researchers who help improve security may be acknowledged here (with permission).

Logos, colours and usage guidelines for showing EliTechZ on partner, client, event and press pages.